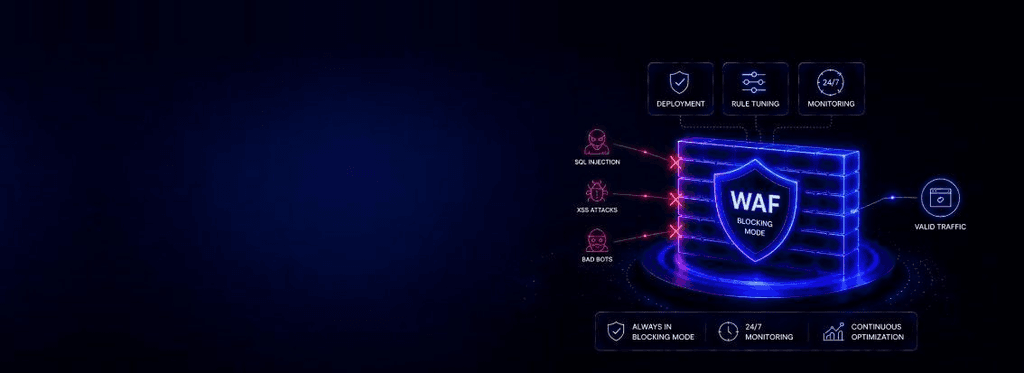
Deployment, rule tuning and 24/7 monitoring - so your WAF stays in blocking mode instead of monitor-only.
Most web application firewalls are deployed once, left in default configuration, and quietly switched to monitor-only mode the first time they block a legitimate customer transaction. At that point the WAF is a compliance artefact rather than a control. It logs attacks without stopping them, and nobody notices until an incident review asks why.
Vinca Cyber's managed WAF service exists to prevent exactly that outcome: deployment, ongoing rule tuning and 24/7 monitoring, so your web application firewall actually blocks attacks in production. It's part of the same 360° Cyber Resilience approach we've applied for 9 years, and it extends the web application security layer already included in our Managed Security Services.
Inspects HTTP traffic and blocks injection, XSS, credential stuffing, bots and app-layer DoS.
WAF as a service runs from the cloud; managed WAF adds ongoing rule ownership and response.
Effectiveness depends on how well rules are maintained — not which product you bought.
Out-of-the-box WAF rules are either too permissive or too aggressive. The tuning cycle is where the value sits.
Implementation in blocking mode, sized to your traffic and application architecture.
Custom WAF rules written for your specific applications, beyond the generic OWASP core rule set.
The work that determines whether a WAF stays in blocking mode or gets quietly disabled.
Blocked-traffic review and attack investigation by our SOC.
Application-layer protection against automated abuse and credential stuffing.
WAF rules deployed to block exploitation of a known application vulnerability while your developers work on a permanent fix.
Out-of-the-box rules are either too permissive or too aggressive for your real traffic.
Value sits in continuous tuning: fix false positives, add app-specific rules, revisit when features ship.
Most in-house teams lack capacity to own that cycle — which is what managed WAF covers.
Implement WAF in blocking mode, sized to your traffic and architecture.
These programmes are designed to be operated together. If this page is the strand you need first, the others are usually next.
CSPM, CNAPP and 24/7 monitoring across AWS, Azure and GCP, with cloud security solutions and cloud security tools that provide posture visibility beyond the assessment.
DLP, data security, database security and GenAI leakage protection - so sensitive data doesn't leave through a chat window.
Protect business email with email security, phishing filtering, and domain authentication controls that help prevent spoofing and keep malicious messages out of your inbox.
Managed EDR/XDR with 24/7 response, backed by endpoint security controls so a phished laptop doesn't become a full network compromise.
Protect your network with firewall security services, including next generation firewall solutions, ongoing firewall management services, policy tuning and continuous monitoring.