Managed EDR/XDR with 24/7 response, backed by endpoint security controls so a phished laptop doesn't become a full network compromise.
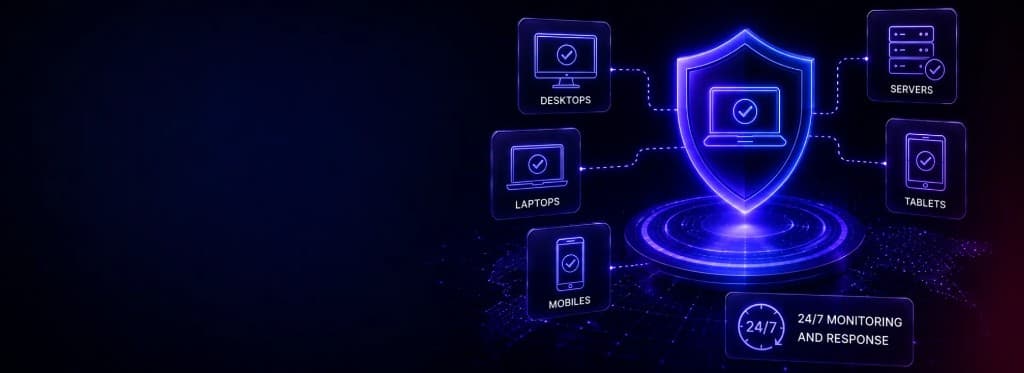
Every laptop, server and mobile device your team uses is a potential entry point. With hybrid work, BYOD policies and cloud synced environments, the number of endpoints organisations need to protect continues to grow.
Endpoint security helps prevent a compromised device from becoming a wider network incident.
Vinca Cyber's endpoint security practice combines next generation antivirus, EDR and XDR with 24/7 monitoring, bringing security operations to every device across your environment. Our capabilities are supported by partnerships with Cynet and Palo Alto Cortex XDR.
Protect laptops, desktops, servers and mobile devices from malware, ransomware, exploits and fileless attacks with endpoint security.
EDR investigates threats already present on a device, while XDR correlates endpoint signals with network, cloud and identity environments.
EPP blocks known threats, while EDR focuses on detecting and responding quickly when something gets through.
Every engagement is backed by our 24/7 managed SOC, so endpoint alerts are investigated and acted on without unnecessary delays.
Continuous endpoint monitoring and automated response through Cynet's all in one platform and Palo Alto Cortex XDR.
Our SOC investigates and contains endpoint alerts around the clock, not just during business hours.
Behavioural detection and lateral movement deception designed to stop ransomware before it spreads.
Endpoint layer controls that reduce the attack surface exposed by browsers and locally installed applications.
Rollout, policy tuning and false positive reduction across your device fleet, not just a licence handover.
Periodic testing to confirm your endpoint security software is detecting and blocking the threats it is designed to catch.
App and web controls protect what you build, while endpoint security protects the devices your people use.
Firewalls enforce controls at the network layer, while endpoint agents handle threats that reach the device itself.
Built for managed fleets with central policy and 24/7 response, not consumer single device antivirus.
Review current endpoint protection solutions and identify gaps across your device fleet.
These programmes are designed to work together. If endpoint security is where you need to start, the other solutions can follow as your security requirements evolve.
CSPM, CNAPP and 24/7 monitoring across AWS, Azure and GCP, with cloud security controls that continue beyond the initial assessment.
DLP, database security and GenAI leakage protection designed to strengthen data security and help prevent sensitive information from leaving through a chat window.
SPF, DKIM and DMARC enforcement plus phishing filtering, supported by email security controls to help prevent domain spoofing and malicious mail.