DDoS protection, application security, API security, resilience testing and tested recovery help keep critical applications available during attacks and disruption.
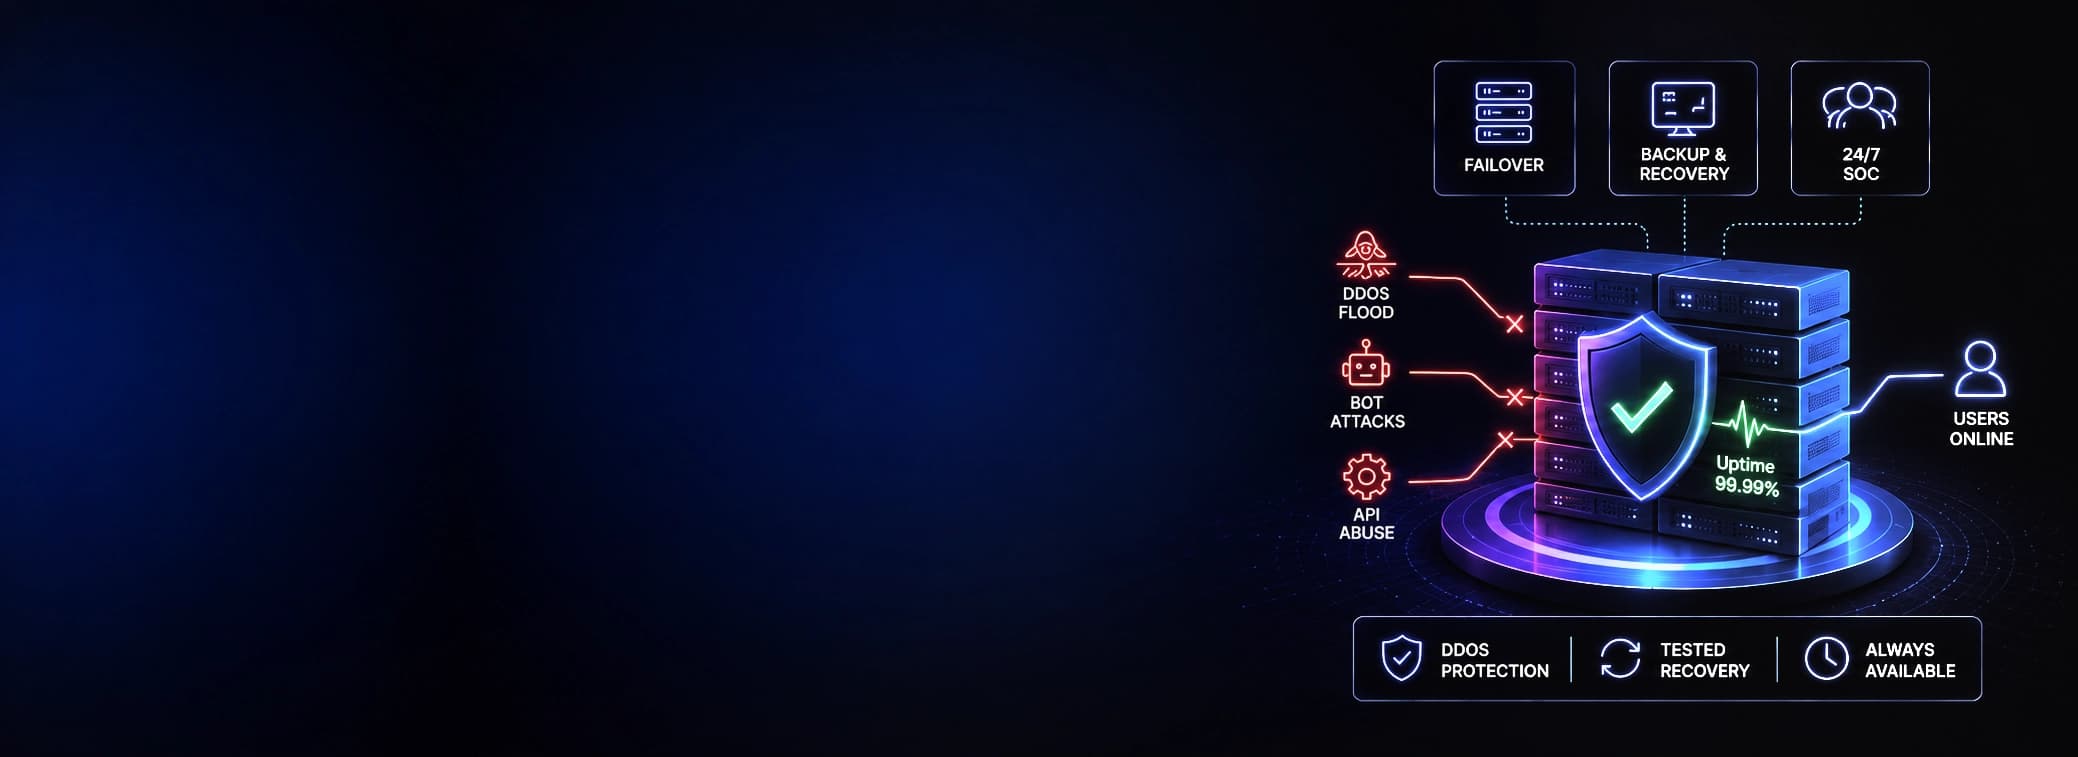
Your customers never see your security infrastructure; they only see whether your application works. Application resilience helps critical applications remain available, secure and recoverable during attacks, outages and unexpected disruption.
The discipline combines application security tools, resilience testing and reliable recovery into a managed approach supported by continuous security operations.
Application resilience means keeping applications available, secure and recoverable when they face attacks, failures or unexpected traffic. It considers how applications, APIs, databases and third party services perform under stress, and how quickly services can recover when disruption occurs.
It works alongside web app security tools and other security controls to reduce application risk while supporting reliable recovery.
Attack protection, resilience testing and reliable recovery combined into a single managed service.
Map critical applications, their dependencies and single points of failure, and agree realistic recovery time and recovery point objectives with business owners.
Network and application layer protection against malicious traffic, credential stuffing and automated abuse.
Discover exposed APIs, including undocumented endpoints, with schema enforcement, rate limiting and abuse detection.
Managed waf rules that stay in blocking mode, with virtual patches that shield known application flaws while developers fix the code.
Controlled load, failover and simulation exercises that show how applications behave under pressure before a real disruption occurs.
Immutable backups for application data and scheduled restore drills that validate recovery within agreed objectives.
Application telemetry fed into our SOC, with response playbooks for application attacks, ransomware and data tampering scenarios.
Regulators are placing greater focus on business continuity, recovery procedures and security controls. Organizations need security programs that can identify risks, protect critical applications and maintain reliable recovery processes.
Application attacks can disrupt customer facing services through credential abuse, malicious traffic and API attacks. Application resiliency engineering services help organizations prepare for disruption and strengthen how critical applications respond, recover and remain available.
Application resilience works alongside the security services you already use. VAPT / penetration testing identifies vulnerabilities that could be exploited, while application resilience focuses on keeping critical applications available and recoverable when disruption occurs.
Managed security services provide ongoing security operations that bring these capabilities together, helping organizations continuously monitor, respond and improve their security environment.
Identify the applications that earn revenue or carry regulated data, and trace every dependency behind them.
These programmes are designed to be operated together. If this page is the strand you need first, the others are usually next.
CSPM, CNAPP and 24/7 monitoring across AWS, Azure and GCP, with cloud security governance that continues beyond assessment.
DLP, database security and GenAI leakage protection to keep sensitive information protected across your environment.
SPF, DKIM and DMARC enforcement with email security tools and phishing filtering to reduce malicious email risks.