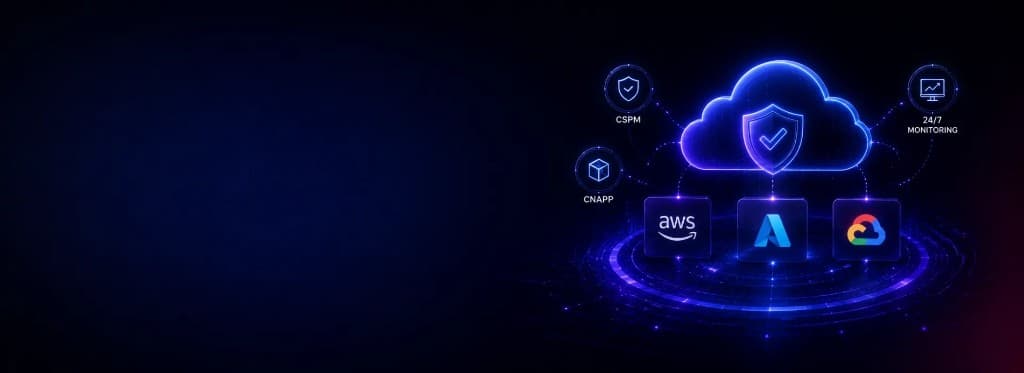
CSPM, CNAPP and 24/7 monitoring across AWS, Azure and GCP, with cloud security solutions and cloud security tools that provide posture visibility beyond the assessment.
Moving to the cloud didn't remove your attack surface. It just moved it, and split it across a dozen consoles your security team may not fully see. A single misconfigured storage bucket or over-permissioned identity role can undo years of on-prem hardening in minutes, which is why cloud security is now one of the fastest-growing areas of client demand we see.
Vinca Cyber's cloud security practice brings the same 360° Cyber Resilience model we've used for 9 years to AWS, Azure and Google Cloud environments, combining posture management, workload protection, cloud security solutions and 24/7 monitoring, supported by cloud security tools delivered through our partnerships with Netskope, Check Point and Palo Alto Cortex Cloud.
Policies and controls that protect data, apps and infrastructure in cloud security solutions across AWS, Azure, GCP or hybrid environments.
CSPM continuously scans for misconfigurations using cloud security tools against frameworks like CIS and ISO 27001.
CNAPP extends that visibility into containers, workloads and the application layer itself.
Vinca Cyber's cloud security solutions cover the full stack. Each engagement blends automated cloud security tools, including cloud vulnerability assessment tools, with hands-on review, so findings reflect real exploitability and map to practical solutions your team can actually implement with cloud security governance.
Continuous configuration and compliance scanning across AWS, Azure and GCP, supporting cloud security governance.
Runtime protection for VMs, containers and serverless functions via Palo Alto Cortex Cloud, using cloud security tools.
Data and threat protection for SaaS and cloud traffic through our Netskope partnership, delivering cloud security solutions.
Check Point-backed perimeter and micro-segmentation controls through firewall security services.
A cloud-focused extension of our Vinca Cyber 360° Assessment Service, using purpose-built cloud vulnerability assessment tools alongside manual validation.
Public storage buckets, over-permissioned identity and access management (IAM) roles and unencrypted data in secondary accounts.
Security groups left wide open from testing, and shadow cloud accounts outside IT's view, creating cloud security governance gaps.
Gaps that need no sophisticated attacker — they're the first things our assessments look for.
Manual validation of the highest-risk findings using cloud security tools
Ongoing 24/7 monitoring with drift alerting for managed clients, supporting continuous vulnerability management
Prioritized remediation roadmap ranked by business impact
CSPM scan benchmarked against CIS Benchmarks and ISO 27001 cloud controls for cloud security governance
Full cloud asset inventory across every account, subscription and project you authorise, providing asset visibility
Map your full cloud footprint across accounts, subscriptions and projects, including shadow IT.
These programmes are designed to be operated together. If this page is the strand you need first, the others are usually next.
DLP, data security, database security and GenAI leakage protection - so sensitive data doesn't leave through a chat window.
SPF, DKIM and DMARC enforcement plus email security and phishing filtering - so your domain can't be spoofed and malicious mail doesn't land.
Managed EDR/XDR with 24/7 response - so a phished laptop doesn't become a full network compromise through endpoint protection solutions.