Discover, prioritize and remediate vulnerabilities through continuous vulnerability management, helping your organization identify security gaps and address them before they become serious risks.
Most organisations don't have a vulnerability detection problem. They have a remediation problem. Scanners produce thousands of findings, while teams struggle to identify which vulnerabilities require immediate action. Our vulnerability management approach prioritises real risk, supports remediation and helps reduce exposure across your environment.
Vinca Cyber's vulnerability management practice closes the loop from discovery and risk based prioritisation to remediation and verification. With continuous vulnerability management, your security team gets an ongoing process for identifying, prioritising and addressing vulnerabilities rather than relying on periodic reports.
Vulnerability management is an ongoing cycle of discovering, prioritising, remediating and verifying vulnerabilities based on actual risk.
New assets and vulnerabilities appear continuously, so continuous vulnerability management helps maintain visibility beyond a one time assessment.
Remediation is not limited to patching. Depending on the vulnerability, teams may require configuration changes, compensating controls or other remediation measures.
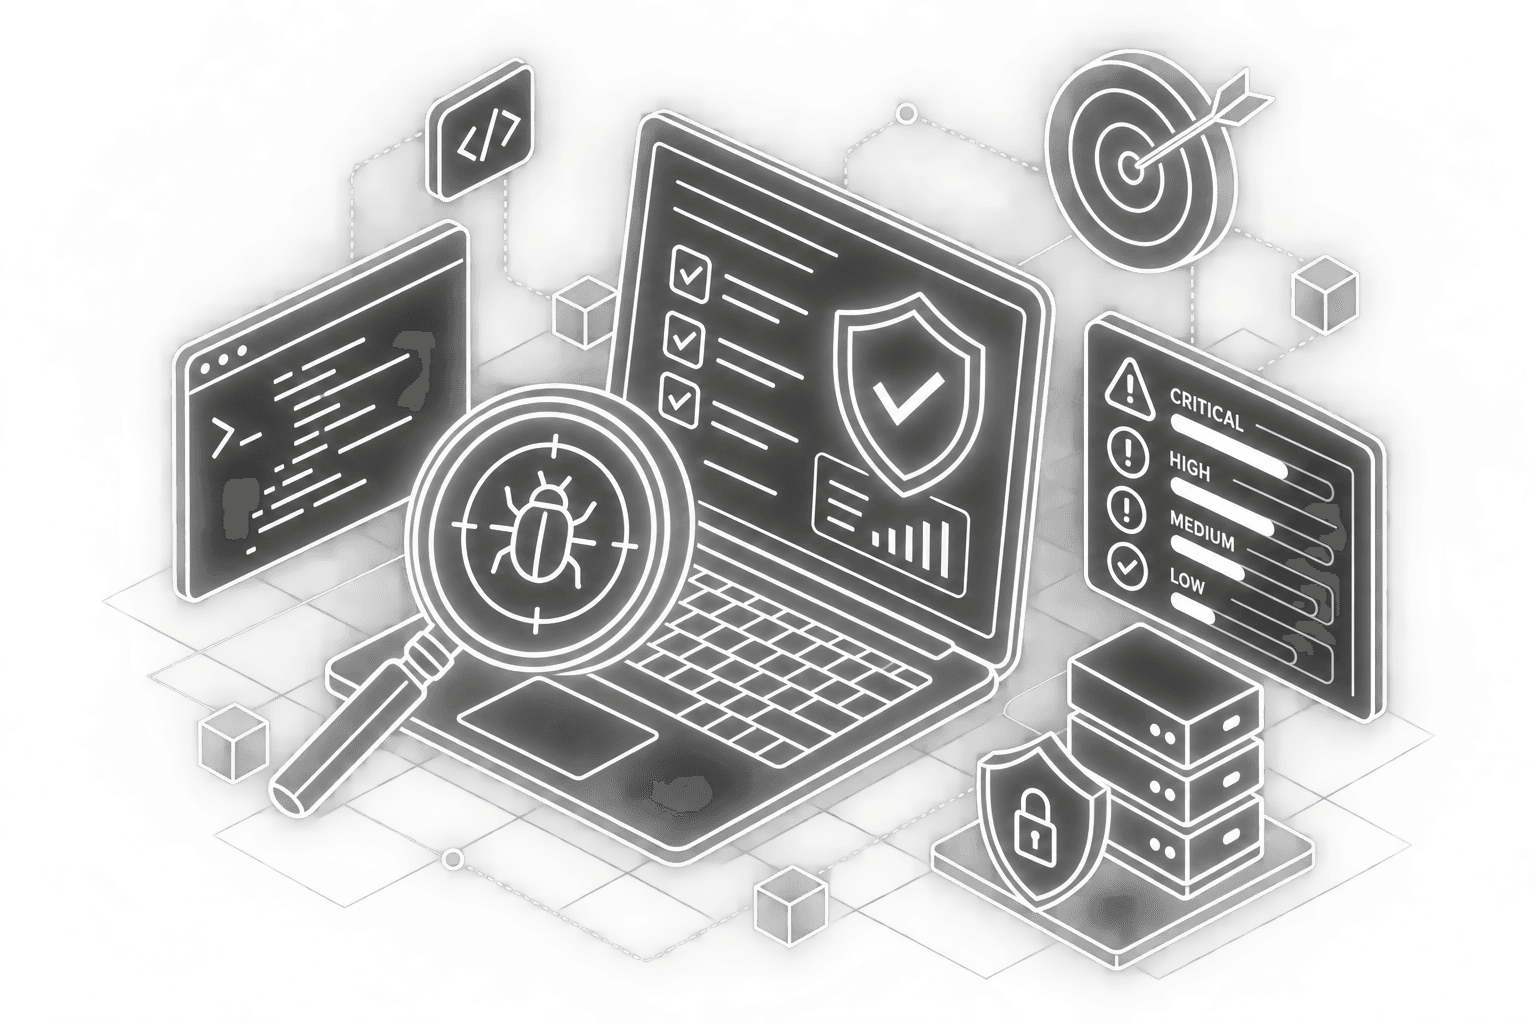
Continuous discovery through verified remediation, combining vulnerability management with patch management services to identify, prioritize and address security weaknesses across your environment.
Continuous discovery across servers, workstations, applications and cloud workloads to maintain visibility into vulnerabilities across your environment.
Prioritize vulnerabilities based on asset criticality and real exploitation risk, so remediation efforts focus where they matter most.
Patch management services for Windows, macOS and Linux, covering operating systems and third party applications.
Protect vulnerable applications when immediate patching is not possible, reducing exposure until a validated fix becomes available.
Automated remediation for configuration issues, registry changes and file level vulnerabilities that require fixes beyond patching.
Verify that vulnerabilities are actually resolved, not simply that a patch was deployed, as part of continuous vulnerability management.
New assets and vulnerabilities are identified as they appear, not months later at the next audit.
Remediation becomes a steady process instead of a pre audit scramble.
Show auditors, clients and insurers that exposure is actively managed, not just periodically measured.
Continuous asset and software inventory across on-premise and cloud environments.
These programmes are designed to be operated together. If this page is the strand you need first, the others are usually next.